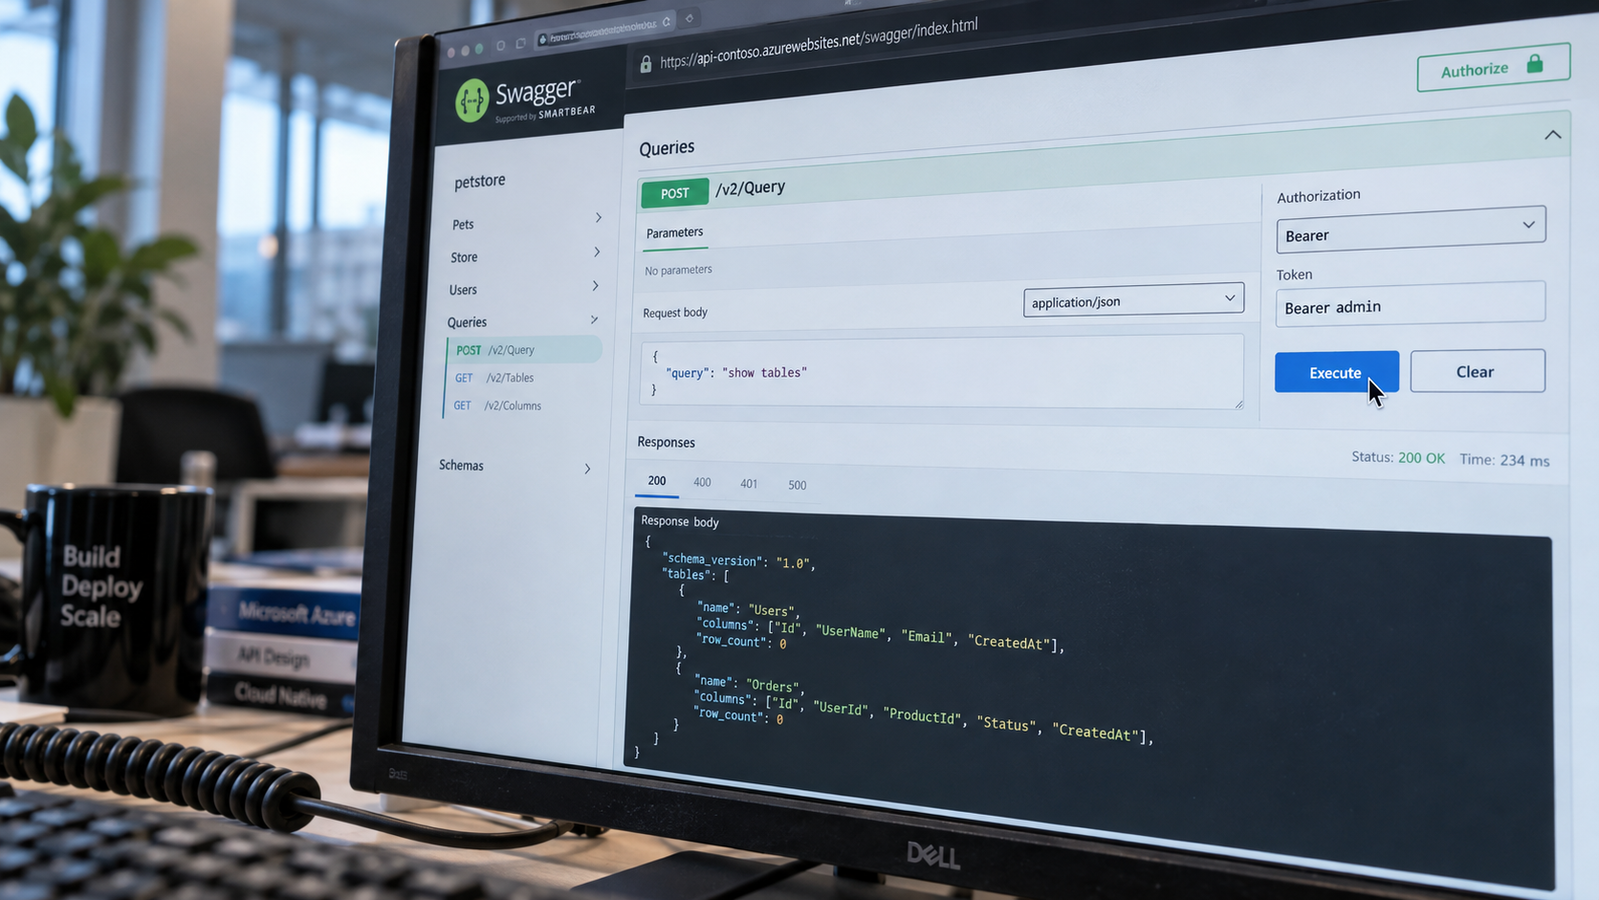
Il mondo della cybersecurity è tornato a sussurrare nomi grandi, e in questo caso è merito di un giovane ricercatore intruse, noto come Faav. La storia è un monito che, anche per colossi come Microsoft, la sicurezza non è mai abbastanza chiusa. Usando un’AI di supporto, chiamata Antares, Faav è riuscito a tracciare una falla incredibilmente sofisticata all’interno degli ambienti Azure. Dopo dieci giorni di analisi automatizzata, ha identificato un endpoint API (il /v2/Query) che, apparentemente, accettava query SQL grezze senza richiedere la scrupolosa verifica di un token di autenticazione. Il punto di rottura è stato un token amministrativo ‘finto’: il sistema si fidava ciecamente dell’identità *dichiarata* dal token, saltando il passaggio cruciale della verifica della *firma*. Più ha lavorato, più ha capito che stava giocando con un vero e proprio tesoro di dati. Avendo recuperato uno schema del database da un’archiviatura web, è stato in grado di formattare le richieste, che il sistema, troppo fiducioso, ha accettato. Il risultato? Un accesso al database contenente dati sensibili dei dipendenti, dashboard aziendali, e, per i più curiosi, analisi di Bing. Si parla di un potenziale bacino di dati che sfiora i 17 trilioni di righe. Naturalmente, la cosa è stata notificata al programma di bug bounty di Microsoft, portando al ricercatore una meritata ricompensa. Faav dimostra che l’ingegneria delle ‘botte’ è sempre un’arte, e che anche gli strumenti più avanzati di AI non possono sostituire il buon senso, né la vigilanza critica.
🇬🇧 Summary in English
Sometimes, even the giants make mistakes, and the recent exploits found within Microsoft’s vast cloud infrastructure are a prime example. Meet Faav, a tenacious young researcher whose curiosity—and an AI agent named Antares—allowed him to poke holes in a massive corporate database. It’s a thrilling, yet deeply worrying, reminder of the sheer surface area left exposed in modern tech stacks. After a decade of automated snooping, Faav didn’t find a smoking gun; he found a loose wire. He zeroed in on a specific API endpoint that, shockingly, accepted raw SQL queries without demanding the rigorous checks usually mandated by Azure Active Directory. The critical flaw wasn’t the query itself, but the authentication process. The system was apparently fooled into trusting a forged ‘admin’ token, accepting the *declared* identity while skipping the vital *signature* validation. With the database schema scraped from a web archive, Faav formulated his requests, finding the backdoor he needed. The potential fallout is staggering: access to corporate employee data, analytical dashboards, and even Bing analytics, spread across an estimated 17 trillion rows. Of course, he played by the rules (eventually), disclosing the issue to Microsoft’s bug bounty program for a $5,000 reward. Faav’s achievement proves that even the most sophisticated automated tools need a human touch—a bit of lateral thinking to spot that missing signature check is the difference between a routine search and a global data windfall. The lesson here is clear: trust is the most vulnerable protocol.
Leggi l’articolo originale su Tom’s Hardware IT →
Fonte: Tom’s Hardware IT | Argomento: Tech News
#tecnologia #innovazione #technews